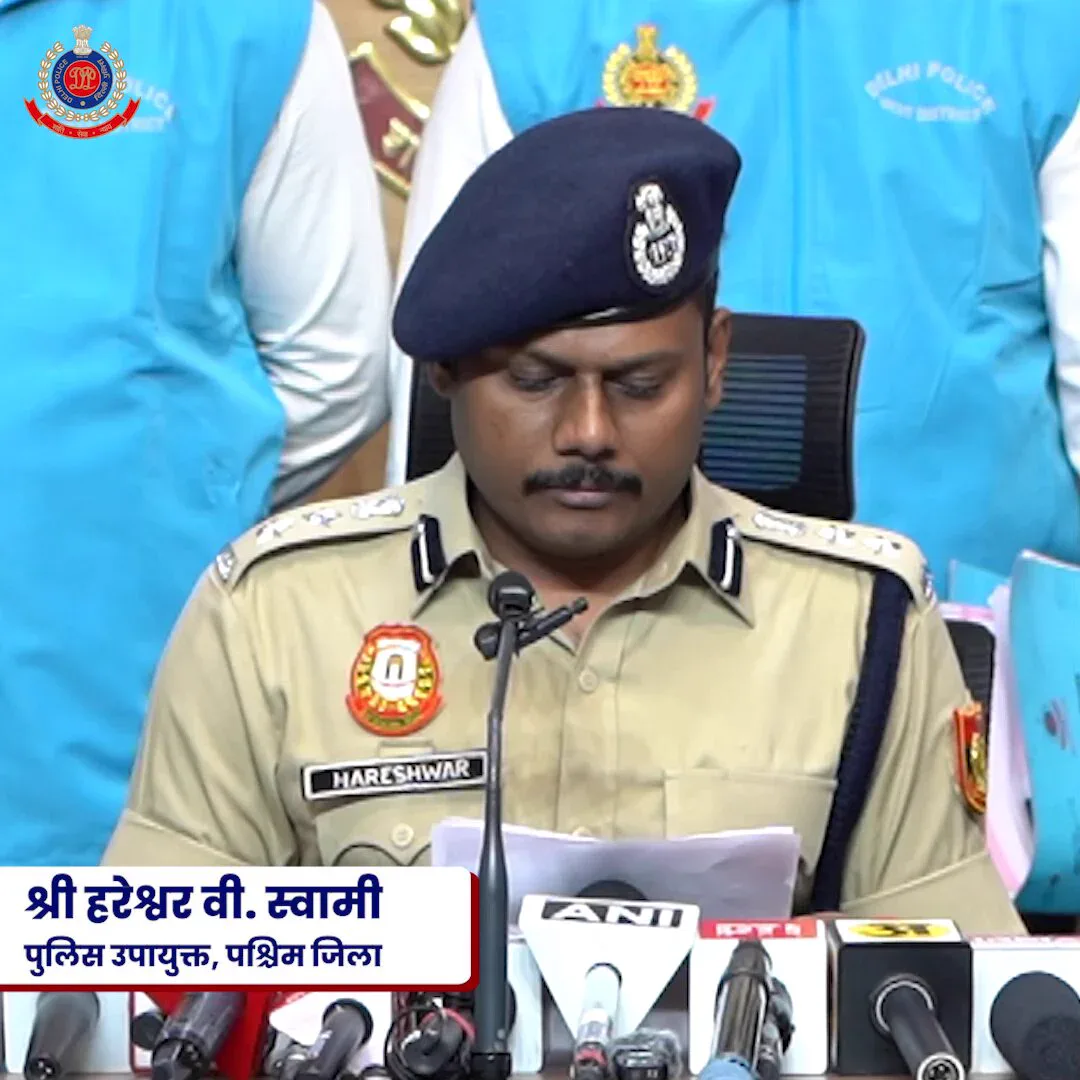
An alleged overseas tech-support fraud network in West Delhi used Apple gift cards among its payment methods, according to police details reported by Press Trust of India. The case places gift cards inside a wider impersonation and payment-collection operation. [S02]
Delhi Police announced on September 18 that officers had arrested 23 people following coordinated raids at three locations. Its official account said the suspects impersonated Apple/iOS and Microsoft technical-support personnel to target people in the United States and Canada. Police reported seizing 27 laptops, 28 mobile phones and other equipment. These are police allegations and arrests, not findings of guilt. [S01]
From a warning on screen to a payment demand
PTI's contemporaneous report, carried by NDTV, dates the raids to September 17. It describes fake pop-ups about unauthorised purchases, subscriptions or security problems directing victims towards toll-free numbers. Callers then allegedly demanded between $149 and $499, with Apple gift cards or Zelle among the payment methods. Police said payment information was circulated within the network for collection and conversion. The account comes from investigators, rather than independently verified victim transactions. [S02]
Why the Apple gift card is the important detail
Apple's gift card is intended for purchases within its own product and service ecosystem. The company's standing fraud guidance says these cards cannot legitimately settle unrelated bills or government payments. It also warns that someone given a redemption code may spend its value before the owner can obtain help. [S03]
The relevant asset is therefore access to the card's value through its code. A physical card need not change hands for that access to be lost. Apple's account of gift-card scams describes criminals directing a victim to buy a card and then disclose its redemption code. That is background explaining the payment risk, not confirmation that every step occurred in each Delhi case. [S03]
Apple and Microsoft occupy two different positions in this account: trusted technology brands allegedly impersonated by callers, and, in Apple's case, the brand attached to one reported payment method. The police announcement does not allege participation by either company. [S01]
The commercial mismatch behind the impersonation
Microsoft's own security guidance describes criminals using fake warnings and remote-access requests to charge for repairs to non-existent problems. It says the company does not make unsolicited support calls and does not request payment for support through gift cards. Its genuine error messages do not contain telephone numbers to call. [S04]
The alleged business mechanism reverses an ordinary customer relationship: the supposed service provider manufactures the problem, claims the authority to fix it, then directs how payment must be made. That is the journalistic significance of the combination of Microsoft's support warnings and Apple's redemption guidance. The brand supplies apparent credibility; the transferable code can supply access to value. This is an explanation of the documented risk, not proof of the suspects' full financial arrangements. [S03][S04]
For gift-card issuers and retailers, the case points to an exposure beyond the checkout transaction itself. A card may be bought through an ordinary retail channel and subsequently misused through a separate conversation. The reporting reviewed does not identify a compromised gift-card platform, disclose a total victim loss or establish the final destination of the alleged proceeds. [S02][S03]
This article is journalistic reporting and analysis, not legal advice.
In this article
Daniel Brooks
Daniel Brooks covers payment networks, financial technology, payment security, gift card fraud and PCI DSS for Gift Card News.