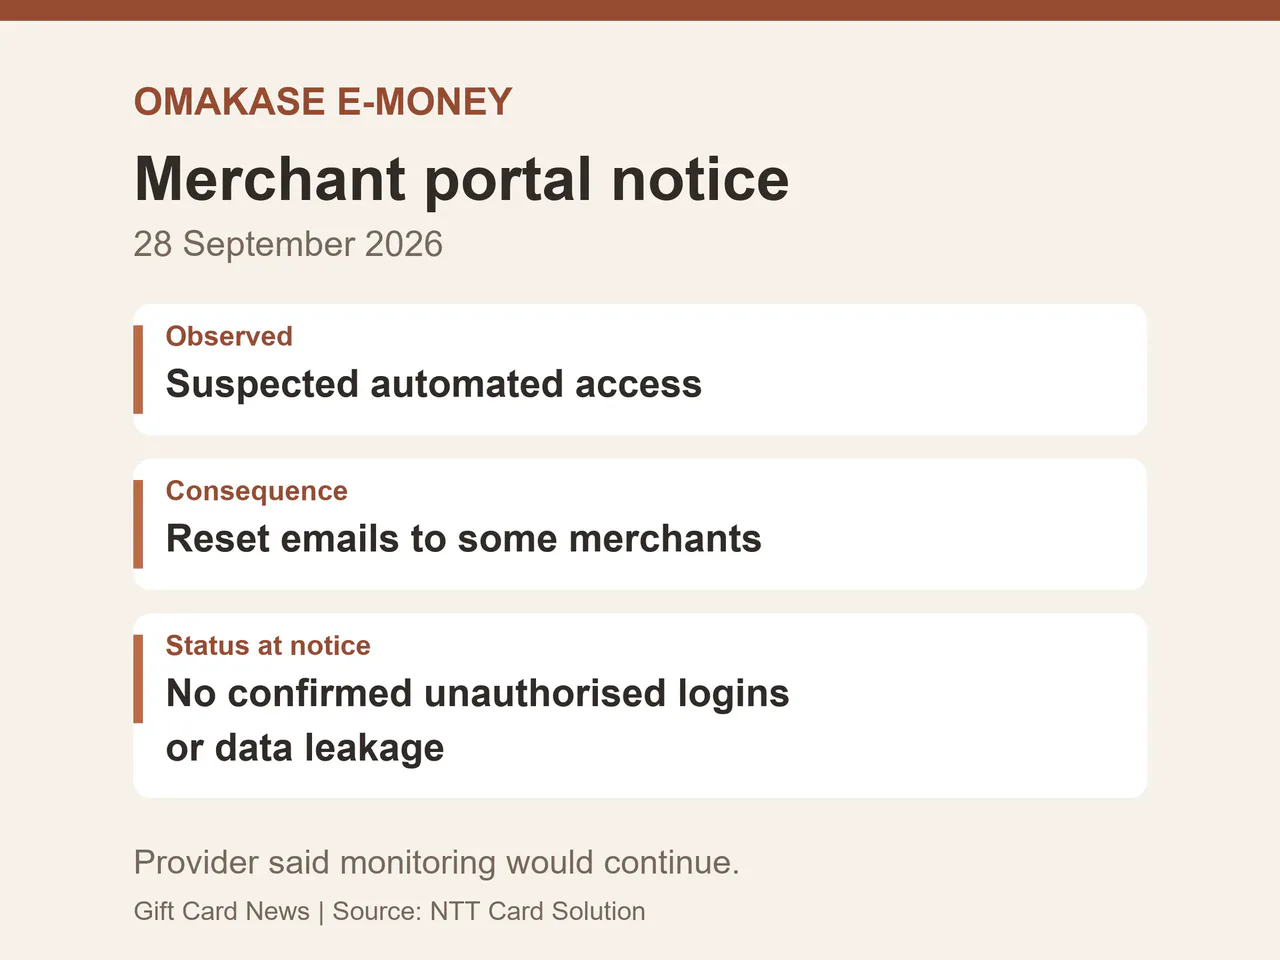
NTT Card Solution has warned merchants using its Omakase e-money regional-voucher platform about suspicious access that appeared to be automated. The September 28 notice said the activity caused password-reset emails to be sent to some participating merchants. [S01]
The provider said it had not confirmed unauthorised logins, information leakage or similar damage at the time of the notice. It did not disclose how many merchants received the emails or when the accesses occurred. [S01]
Merchants receiving reset messages they did not recognise were asked to delete them without opening the links. NTT Card Solution said it would continue monitoring and take measures as necessary. [S01]
Omakase e-money supports locally restricted spending programmes, including premium shopping vouchers, tourism coupons and public-benefit distributions. Its platform covers issuance, QR payments and merchant settlement, with both smartphone and card formats. Participating stores also use the merchant system to manage sales and refunds. [S02]
That operational role makes merchant account access relevant to voucher acceptance and reconciliation. The notice concerns suspicious portal activity and resulting reset messages; it does not establish stolen voucher balances or a confirmed data breach.
In this article
Daniel Brooks
Daniel Brooks covers payment networks, financial technology, payment security, gift card fraud and PCI DSS for Gift Card News.