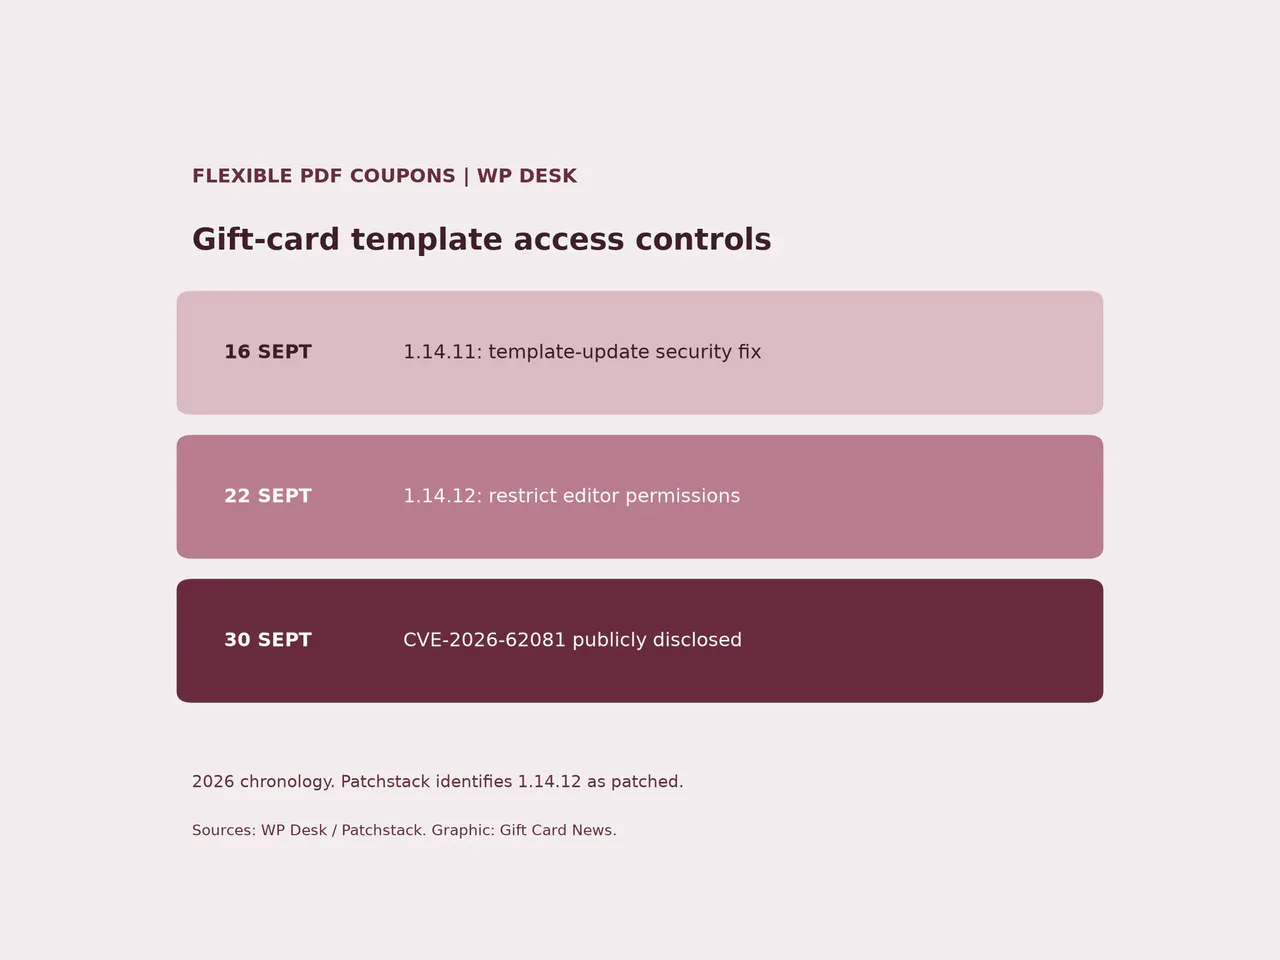
WP Desk tightened access to the template editor in Flexible PDF Coupons, its WooCommerce software for selling and emailing PDF gift cards. Two September releases addressed authorisation controls before Patchstack publicly disclosed a related vulnerability on September 30, 2026. [S01][S02]
The remediation sequence and public download activity
The vendor’s September 16 changelog for version 1.14.11 describes preventing unauthorised template updates. Version 1.14.12, dated September 22, restricted editor access to users with WooCommerce management permissions and corrected Shop Manager access to settings and support. Those dates distinguish remediation from the later public advisory. [S01]
Patchstack identifies versions through 1.14.11 as affected by CVE-2026-62081 and recommends 1.14.12 or later. The CVE record describes an insecure direct object reference requiring Contributor privileges. Patchstack credits researcher Brobicho and records a September 14 report. Its assigned CVSS 3.1 base score is 5.4; that score is a severity assessment, not a count of exploited shops. [S02][S03]
The product places WooCommerce coupon codes into PDF vouchers that merchants can sell and send to recipients. The template editor governs part of that document-issuance workflow. Its control weakness does not by itself establish that an attacker could spend a merchant’s entire gift-card liability. [S01][S03]
The repository’s public series records 484 downloads on September 16 and 648 on September 17. It records 605 on September 22 and 621 on September 23. Those dates coincide with the two vendor releases, but the daily totals do not identify which version was downloaded or why. The complete 21-day series below retains the quieter days as well. [S04]
Daily repository downloads: WP Desk Flexible PDF Coupons
Official daily counts for September 14-October 4, 2026, spanning the security-remediation and disclosure period. Retrieved October 19.
downloads
Tap or hover for details. All values are also available in the data table.
Source
Repository activity, not unique stores, affected installations, gift-card sales or confirmed security updates. The response does not identify downloaded versions, successful installation or exploitation. Date labels are reproduced as returned; the API does not state a reporting timezone. No missing days are filled.
Show data tableHide data table
| Category | Repository-reported downloads |
|---|---|
| 2026-09-14 | 48 downloads |
| 2026-09-15 | 35 downloads |
| 2026-09-16 | 484 downloads |
| 2026-09-17 | 648 downloads |
| 2026-09-18 | 158 downloads |
| 2026-09-19 | 58 downloads |
| 2026-09-20 | 81 downloads |
| 2026-09-21 | 127 downloads |
| 2026-09-22 | 605 downloads |
| 2026-09-23 | 621 downloads |
| 2026-09-24 | 149 downloads |
| 2026-09-25 | 94 downloads |
| 2026-09-26 | 51 downloads |
| 2026-09-27 | 51 downloads |
| 2026-09-28 | 173 downloads |
| 2026-09-29 | 84 downloads |
| 2026-09-30 | 90 downloads |
| 2026-10-01 | 135 downloads |
| 2026-10-02 | 79 downloads |
| 2026-10-03 | 55 downloads |
| 2026-10-04 | 38 downloads |
This is a distribution-activity measure, not proof that 648 separate stores installed a fix on September 17, nor a denominator for calculating patch coverage. The API provides neither individual site identifiers nor an installation-success field. It cannot resolve how many affected installations remained exposed. [S04]
The CVE record rates confidentiality impact as none and integrity and availability impact as low. CISA’s September 30 assessment records no exploitation at that assessment time. Neither that finding nor the download series establishes theft of gift-card balances, customer-data exposure or a merchant loss. [S03][S04]
The verified operational change is the restriction on who can modify gift-card templates and access the editor. The available evidence connects that remedy to dated releases and public repository activity, while leaving affected transaction counts and financial consequences unquantified. [S01][S02][S03]
In this article
Daniel Brooks
Daniel Brooks covers payment networks, financial technology, payment security, gift card fraud and PCI DSS for Gift Card News.